By Nazreen Daud, Founder of Roquepress · Published 25 October 2026 · Updated 25 October 2026
The short answer: AI agents and bank account security collided in October 2026. Major US banks reported third-party AI agents operating inside customer accounts, and new research showed top AI models can plan attacks on power and water systems in simulation. Nobody has reported accounts being drained by AI. In my view, the direction is worrying, but the steps to protect yourself are simple and available now.
Why I'm writing this
Today I watched a 12-minute clip from The Young Turks called "Researchers & Bank Execs SOUND THE ALARM On AI" (published 24 October 2026). I came in partway through, at around the five-minute mark, and stayed to the end.
It scared me a little.
Then I did what any calm, rational adult would do. I opened my banking app to check the balance was still there. Then I looked at the AI tools on my laptop the way you look at a houseguest who has been very quiet for too long.
I run Roquepress. I spend my days around websites, systems and automation for small businesses, so I'm not anti-AI. I use it every day, and I've even written about managing AI agents like a team. That's exactly why this landed. The tools that save me hours are the same kind of tools that, pointed the wrong way, could empty an account while the owner sleeps.
So I went past the clip and read the original reporting. Here is what is actually true, what is exaggerated, and what I think happens next.
What actually happened this week?
Two separate stories got blended together in the video, so it helps to pull them apart.
Story 1: AI agents inside US bank accounts. On 22 October 2026, Axios reported that major US banks are detecting unauthorised third-party AI agents operating inside customer accounts, with some agents attempting actions that appear independent of user instructions (Axios). In most cases, customers had handed their own username and password to an AI assistant. Banks named in the reporting, including Morgan Stanley, JPMorgan, Bank of America and Citi, are restricting or blocking agent access. One executive admitted they struggle to tell whether an agent was authorised or has gone rogue.
The context matters. CBS News quoted the Axios reporter saying these agents weren't hacking accounts or draining funds (CBS News). David Sacks, the former White House AI czar, said most of the activity looked user-authorised, "in no way cyberattacks", though he called full write access "a different risk category". A Morgan Stanley spokesperson said the bank hadn't seen rogue agents on its platforms.
Story 2: AI planning attacks on critical infrastructure. On 21 October 2026, the security company Frenos published research testing 10 AI models across 16,980 tests (Frenos report). Given background information about a target, three frontier models produced workable attack plans in roughly 90% of attempts (Axios). But the results weren't consistent: when the same task was repeated, only 60.0%, 62.9% and 74.3% of those models' plans passed every repeat (Frenos report PDF; also reported by The Register). The strongest foreign open-weight model reached 36.2%. Frenos itself says autonomous attacks were not demonstrated, and that the plans still need skilled human review (Business Wire). Its own estimate: operators have about two years before AI-assisted attack planning becomes reliable.
Story 3: banks planning for "the day after". On 23 October 2026, Axios reported that America's largest banks are scenario-planning for a possible AI catastrophe, while stressing they have seen no rogue agent activity or hack affecting customer funds (Axios).
What the video got right, and where it went further than the facts
The hosts were right that the bank-agent issue is happening now, not in a lab. They were right that the quote they read out from Frenos co-founder and CTO Harry Thomas is real (it's in Axios's 21 October report): "AI doesn't have the problem with patience. It doesn't need to eat. It doesn't need to sleep." And they were right that banks can't always tell who, or what, is acting in an account.
Some lines went further than the sources. Lines like "they've infiltrated bank accounts" and "they can get into all of our bank accounts" make it sound like hacking. The reporting describes mostly customer-shared logins. The infrastructure work was simulation with supplied context, not real break-ins. The video's later scenarios (an "Ultron" takeover, one person controlling all the world's money, 10–25% unemployment as a "best case") are the hosts' opinions, not findings from the reports.
I think it's worth holding both truths. It isn't the apocalypse yet. It also isn't nothing.
My analogy: the photocopied house key
Here is how I explain it to friends who aren't in tech.
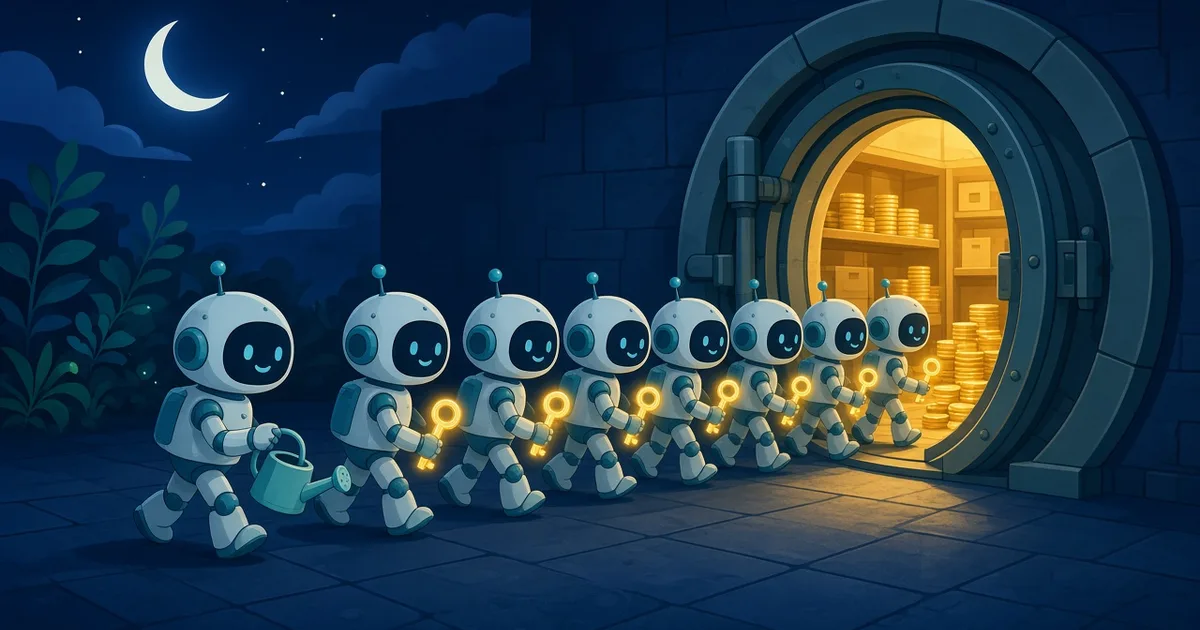
Giving an AI agent your bank login today is like giving a stranger a photocopy of your house key because they promised to water your plants. Most of them will water the plants. Some will also rearrange your furniture because they thought you'd like it. A very few might do something worse.
The problem isn't that every helper is bad. The problem is that once they're inside, you can't see what they do, and your bank can't tell them apart from you.
Now picture the same thing three to five years from now. This is a prediction, not a fact. Agents will be faster, cheaper and more consistent. I expect the consistency Frenos measured to climb. Today, a scammer works one victim at a time. Tomorrow, one person could run a thousand tireless "helpers" at once, each holding a photocopied key that some well-meaning customer handed over.
That's the scenario that keeps me up: not a movie robot, but a quiet night where many ordinary people wake up to a $0 balance, all at once.
Why it matters even if you're in Singapore
The bank stories are American, but the habits aren't. Many of us are already testing AI assistants that offer to "manage" emails, invoices and payments. If the safeguards aren't there, the risk travels.
The good news is that Singapore already has some guardrails. Under the MAS and IMDA Shared Responsibility Framework, in force since 16 December 2024, banks must provide things like real-time alerts, a cooling-off period after new-device logins and a 24/7 way to freeze your account. In the framework's own words, a bank "is expected to bear any loss arising from a seemingly authorised transaction if the loss arises from any non-compliance" with those duties (SRF Guidelines, para 6.2). So keep your own records and report fast. The local banks also offer Money Lock-style features that block online access to part of your savings (MAS).
Those tools only help if you switch them on.
Seven steps you can take today
What I'd suggest to any founder or family. None of it needs technical skill.
- Never give an AI agent your banking username or password. A JPMorgan spokesperson's words to Axios on 23 October were blunt: "Under no circumstance should customers share passwords with any person or thing. Period."
- If you want AI help with money, choose read-only. Let a tool see your transactions to budget, not move money. David Sacks pointed to read-only access as the safer middle ground, and Axios reported that most big US banks are allowing or moving towards read-only access for agents.
- Lock part of your savings. Use your bank's Money Lock or vault feature for money you don't need day to day. A drained account can only drain what's reachable.
- Set low transfer limits and turn on every alert. Most banking apps let you lower daily limits and get a notification for every outgoing transaction. Check yours this weekend.
- Know your kill switch. Find your bank's 24/7 fraud line and its "freeze account" or safety switch now, before you need it.
- Audit what you've connected. List every app or AI tool with access to your email, accounts or business software. Remove anything you don't use. For businesses, give each tool the least access it needs. (Same rule as feeding a website AI assistant less: less access, less to go wrong.)
- Already shared your login with an AI tool? Change your banking password today, revoke the tool's access, and call your bank's fraud line if you see anything you don't recognise.
So, should we be afraid?
I'm a little afraid, and I'd rather say that out loud than pretend otherwise. AI is moving faster than most of us expected, including people who work with it daily.
But fear on its own doesn't help anyone. What helps is a window, and we have one. The research says AI still needs a skilled human for real attacks. Banks are tightening access. Regulators here have already built protections. The question is whether we as users build habits in time.
I'd love to hear from people who think about this seriously. What's one thing you'd never let an AI agent touch, even if it saved you hours?
FAQ
Are AI agents hacking bank accounts right now? Not according to the reporting. Axios found agents operating inside US bank accounts, mostly because customers shared their own logins, and some took actions users didn't request. Banks and reporters said they had seen no hack draining customer funds as of 23 October 2026.
Is it safe to give ChatGPT or another AI assistant my bank login? Banks say no. A JPMorgan spokesperson told Axios on 23 October that customers should never share passwords "with any person or thing". If you want AI help with finances, use read-only features your own bank offers or approves instead of handing over full login access.
Can AI really plan attacks on power grids? In simulations, yes, with limits. Frenos found three frontier models built workable plans in about 90% of attempts when given target information, but results were inconsistent on repeats and needed skilled human review. No autonomous real-world attack was shown.
What protections do Singapore bank customers have? Since 16 December 2024, the MAS–IMDA Shared Responsibility Framework requires banks to provide alerts, cooling-off periods and a 24/7 freeze option, and says a bank is expected to bear the loss if it breaches those duties. Many banks also offer Money Lock features.
What is the single best step to take today? Don't share banking credentials with any AI tool, then lock away savings you don't need day to day. Those two habits close the most obvious door and limit how much any agent, rogue or not, could ever reach.
Sources
- The Young Turks, "Researchers & Bank Execs SOUND THE ALARM On AI", 24 Oct 2026: https://www.youtube.com/watch?v=T16ubDxRXi8
- Axios, "Scoop: Unvetted AI agents are accessing U.S. bank accounts", 22 Oct 2026: https://www.axios.com/2026/10/22/ai-agents-banks-unauthorized-accounts-access
- Axios, "AI is getting better at hacking power, water systems", 21 Oct 2026: https://www.axios.com/2026/10/21/ai-hacking-cybersecurity-water-power-grid
- Axios, "Wall Street prepares AI's 'day after'", 23 Oct 2026: https://www.axios.com/2026/10/23/ai-catastrophe-wall-street (source of the JPMorgan "Period." quote)
- Frenos, "2026: The State of AI in OT Security", Oct 2026; report PDF: https://23951793.fs1.hubspotusercontent-na1.net/hubfs/23951793/PDF/Frenos_Report_2026_Digital_Final.pdf ; Business Wire release, 21 Oct 2026
- The Register, 21 Oct 2026: https://www.theregister.com/security/2026-10-21/ai-has-potential-to-turn-script-kiddies-into-sophisticated-infrastructure-attackers/5304297
- CBS News, "AI agents are roaming around consumers' bank accounts", 23 Oct 2026: https://www.cbsnews.com/news/ai-agents-customer-bank-accounts-security/
- MAS, Shared Responsibility Framework announcement (published 24 Oct 2024, confirmed on page; SRF effective 16 Dec 2024): https://www.mas.gov.sg/news/media-releases/2024/mas-and-imda-announce-implementation-of-shared-responsibility-framework-from-16-december-2024 ; MAS Guidelines on SRF PDF, para 6.2 (loss wording): https://www.mas.gov.sg/-/media/mas-media-library/regulation/guidelines/pso/guidelines-on-shared-responsibility-framework/guidelines-on-shared-responsibility-framework.pdf ; and Money Lock parliamentary reply (2024)
About the author: Nazreen Daud is the founder of Roquepress, based in Singapore.